
Easily meet the automation mandate for FedRAMP 20x. Automatically collect evidence, validate KSIs in real time, and give internal and external stakeholders continuous visibility into your security posture.




Static security documents that are outdated the moment they’re written. Assessed only once a year.
Automate measurable, transparent proof that your environment is secure right now and historically.
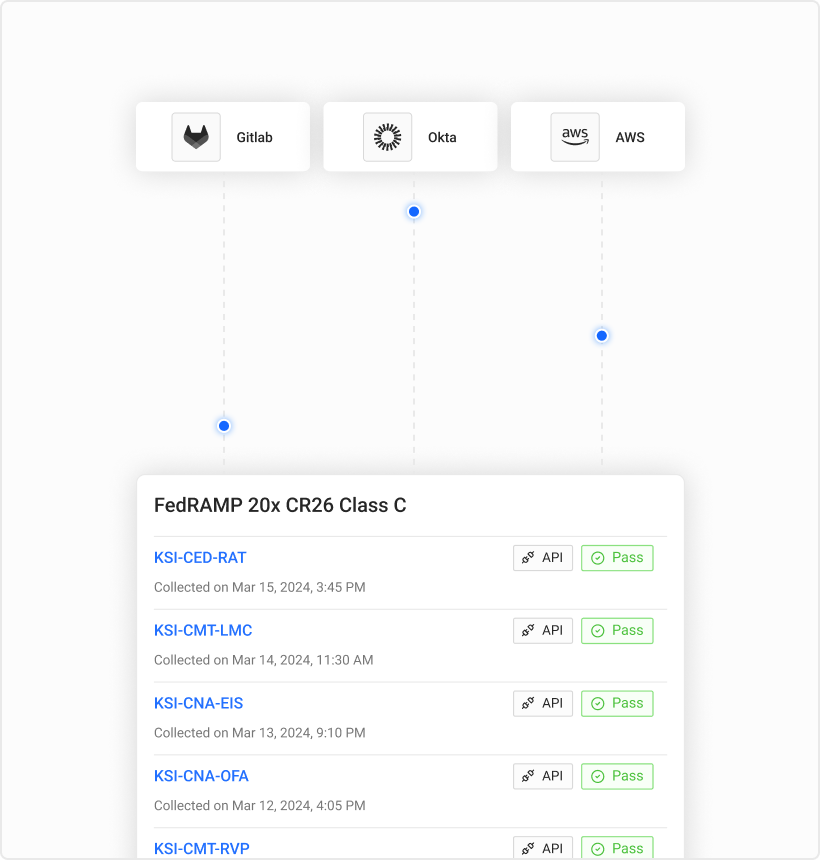

Paramify's automated evidence fetchers securely pull directly from your systems, turning live system state into structured, audit-ready evidence compliant with FedRAMP 20x requirements.

Nothing leaves your infrastructure except the evidence itself, so your data stays yours.

Every fetcher feeds its own living Evidence Set. Each collection cycle appends fresh artifacts automatically, so the evidence behind a KSI is always current.
Replace point-in-time reviews with continuous validation. Uncover security gaps long before audit season and automatically convert failed checks into actionable issues.
Ensures every relevant resource is configured and monitored, providing continuous, real-time proof of compliance.
Automatically validate your environment against FedRAMP KSIs and broader risk management requirements for an instant, pass/fail view of your security posture.
When a check fails, Paramify flags the gap, links the failed artifact to the exact KSI, and dispatches a ticket straight to the owner in Jira, ServiceNow, or GitLab, eliminating manual spreadsheet tracking and keeping your true security posture always in view.

UberEther cut assessment labor hours by 80% and scaled compliance capacity 400% after moving off manual evidence collection.

Gaps surface continuously instead of surfacing at audit time, when they're expensive and public.

Evidence and its validation status are always current, not reconstructed under deadline pressure.

Used by nearly half of all FedRAMP certified companies to automatically generate accurate compliance packages.
CR26 rule FRC-CSX-VVK sets the bar by certification class: Class A providers may use automated verification, Class B should use at least one automated method per KSI, Class C must use at least two independent automated methods per KSI, and Class D must use at least four. Paramify's Fetcher/Validator pairings are built so that using more than one pairing against the same KSI moves you toward — or past — that method bar without extra manual work.
No. Fetcher scripts and the secrets they use run entirely in your customer-controlled environment (a Docker container, AWS Lambda, EKS, etc.) — not inside Paramify. Only the resulting evidence artifact is sent to Paramify. Nothing else leaves your infrastructure.
Validation Rules provides transparency for assessors by surfacing exactly how evidence was automatically validated. It shows pass/fail/partial results with the underlying evidence artifact attached, allowing auditors to trust see exactly how the control implementation validation functions.
20x requires continuous assessment of your tool so agencies can get a more real-time understanding of your security posture.
With Paramify you can automatically retrieve, store, and validate the evidence required for continuous assessment of your FedRAMP 20x KSIs.