What Happens If You Miss the December 7 FedRAMP VDR Deadline? The Grace Period, Explained

FedRAMP’s VDR and VER rules become required on December 7, 2026, and certified providers who aren’t following them by March 7, 2027 lose certification until they are.

Isaac Teuscher
|
53
min read

In This Article

December 7 is close enough that the real question is no longer how to be ready. It's what happens if you aren't. The short version: nothing happens on December 8. You enter a grace period that ends March 7, 2027, and that date is a hard stop that your progress, your plan, and FedRAMP's awareness of both will not move.

Our team walked through the consequences in the video above. Read on to learn what FedRAMP's deadline tiers actually mean, the remediation timeframes by certification class that nobody tells you to go look up, and whether losing certification is permanent.

What is the December 7 VDR deadline?

December 7, 2026 is the date the FedRAMP Vulnerability Detection and Response (VDR) and Vulnerability Evaluation and Reporting (VER) rulesets become required. 

FedRAMP moved them forward from the rest of the 2026 Consolidated Rules in NTC-0014, to line up with CISA Binding Operational Directive 26-04. 

Both rulesets now carry the tag "Required (Mandated by CISA BOD 26-04)" on their rule pages.

A reminder, since they’re regularly confused. VDR is Vulnerability Detection and Response. VER is Vulnerability Evaluation and Reporting. Detection and response in one, evaluation and reporting in the other. They are separate rulesets with separate rule IDs. 

→ Confused? Learn more about the difference between VDR and VER. 

What FedRAMP VDR/VER deadlines actually mean

FedRAMP's Important Deadlines page shows you’re going to need VDR/VER in place for any new application after Dec 7. If you’re working toward FedRAMP Certification, you cannot overlook this. 

Any currently FedRAMP Certified system also needs to get it implemented by then, with a grace period through March. After March, your certification is at risk.  

Milestone VDR and VER date What it means
Obtain December 7, 2026 You must already be following the rules to get a new certification after this date
Maintain December 7, 2026 Active certifications must be following the rules to keep certification; corrective action will be requested after this date
Grace Ends March 7, 2027 Offerings not following the rules by this date lose their FedRAMP Certification until they follow them

Source: the VDR and VER rulesets and the Important Deadlines page.

What the VDR grace period does and does not buy you

Between December 7 and March 7 you keep your certification and keep operating. FedRAMP will request corrective action, your agency customers join the conversation, and you bring forward a plan describing how you will meet the requirements you are missing and by when. FedRAMP does not hand you this plan, you’re going to need to develop your own.

FedRAMP's language doesn’t mess around:

"There will be no extensions past the ending of the default grace period. The default grace period is a hard deadline that applies regardless of notification, corrective action, or progress."

I think they’re serious. 

A corrective action plan does not extend March 7. Visible progress does not extend March 7. Not having been formally notified does not extend March 7. 

There’s no negotiation in the grace period. It’s a countdown so you can keep selling while you get your system up to date, but time is ticking.

If FedRAMP determines you are not following the rules at the end of it, FedRAMP "will revoke their FedRAMP Certification with public notice."

Beat the deadline with Paramify.

Get VDR-ready

Is losing certification permanent?

Not so much. FedRAMP's deadlines page says that it "will take no other punitive action, and cloud service offerings that lose their FedRAMP Certification in this way can regain it by demonstrating they are following the rules."

So revocation can be a temporary state while you get your program in place. 

Basically, you are out until you can show you are in. Unfortunately, a gap in certification can mean lost contracts. We don’t recommend risking it. 

What you need to know to be VDR Ready by December 7

1: Your certification class 

VDR and VER are published per class, and the remediation timeframes are not the same at each one. If you are reading someone else's summary of the rules, check which class it describes.

2: Your remediation timeframes 

These are the numbers nobody quotes, and they are the whole substance of the requirement. Each is measured from evaluation, and depends on the PAIN rating plus whether the vulnerability is likely exploitable (LEV) and internet-reachable (IRV).

Source: VDR-TFR-PVR on the Class B, Class C and Class D VDR rulesets. Longer timeframes apply when a vulnerability is not internet-reachable or not likely exploitable.

3: LEV, IRV, & the PAIN scale
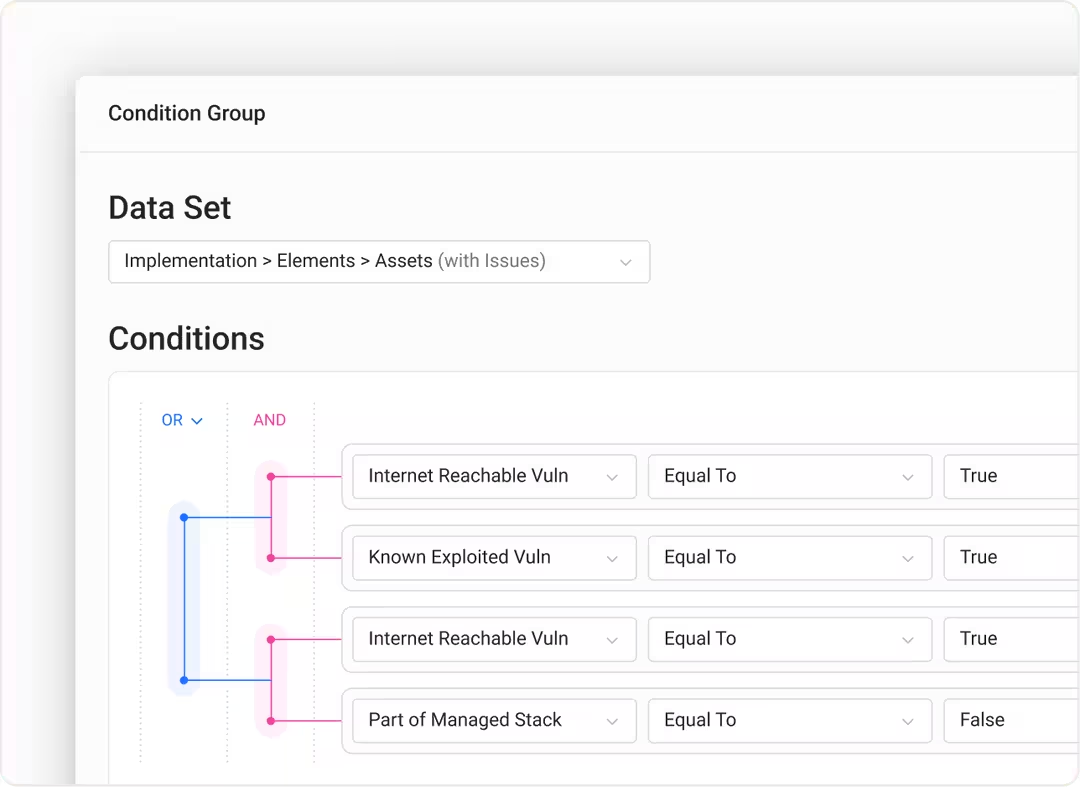
Likely exploitable, internet-reachable, and PAIN. Every finding gets measured by all three. The combination is what selects the row and column above. Internet-reachable in particular is broader than publicly accessible, which we covered in our VDR explainer.

4: Your reporting 

You’re going to need to provide the following: 

  • Human-readable activity reporting at least monthly is a MUST under VER-TFR-MHR.
  • Persistent reporting of detection and response activity is a MUST under VER-RPT-PER. 
  • Under VER-TFR-MAV, you MUST categorize any vulnerability that will not be fully mitigated or remediated within 192 days of evaluation as an accepted vulnerability. 

What this means for your FedRAMP program

December 7 marks the end of the cycle time you’ve been used to. 

A two-day window on a PAIN-5 finding that is likely exploitable and internet-reachable is not a window a monthly process can hit. Neither is it one you can hit if labeling a finding with its PAIN rating and reachability takes a person an afternoon of reading. 

The requirement is not really "patch faster," it is "know what you are looking at within hours of finding it."

That is also why the grace period is less useful than it looks. Three months is enough time to write a corrective action plan and not enough to rebuild a vulnerability management pipeline from scratch while running it.

 Providers who treat December 7 as the date they start are the ones for whom March 7 arrives as a surprise.

A two-day window doesn't wait for a monthly process. Paramify gets your VDR program ready.

Get VDR-ready

Key takeaways

Nothing happens on December 8.

Missing December 7 puts you in a grace period, not out of certification, and you keep operating through it.

March 7, 2027 is a hard deadline.

There are no extensions after this date, and it applies regardless of notification, corrective action, or progress.

Put together your corrective action plan.

FedRAMP requests it after December 7 and brings in your agency customers, but it does not buy additional time.

Revocation is reversible.

FedRAMP takes no other punitive action, and an offering that loses certification this way can regain it by demonstrating it follows the rules.

December 7 is also the Obtain date.

Providers applying for a new certification must already be following VDR and VER.

Know your class before anything else.

PAIN-5 remediation on a likely exploitable, internet-reachable finding is 4 days at Class B, 2 days at Class C, and 12 hours at Class D.

How Paramify helps with the VDR and VER deadlines
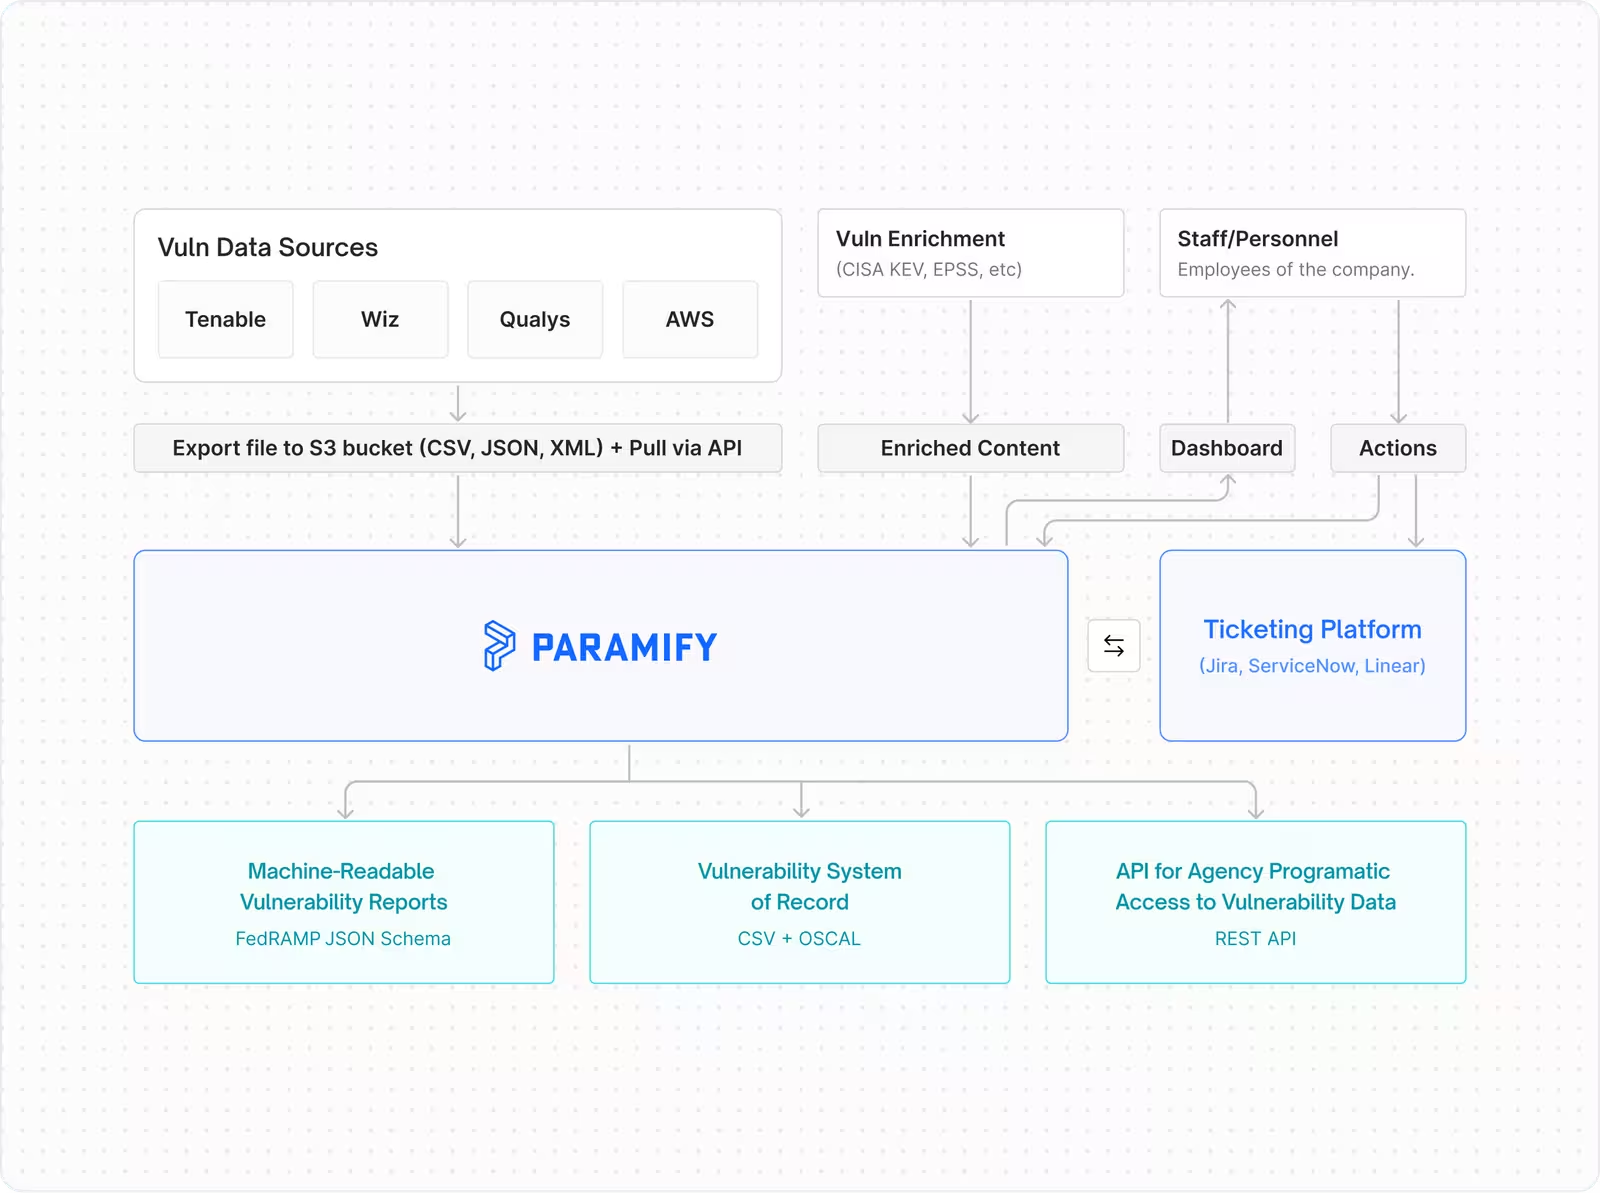
The deadline demands a pipeline that can take a scan file and come back with, per finding, a PAIN rating, an internet-reachability determination, and an exploitability judgment, fast enough that a two-day window is survivable.

Paramify ingests vulnerability scan output and applies your environment's business logic to it: which resources sit on a path that processes internet payloads, which findings are likely exploitable in your architecture, and what the realistic impact on an agency customer would be. 

The remediation clock then runs against the timeframe that combination selects for your class rather than against a generic severity score. The monthly human-readable report and the machine-readable historical record generate from the same underlying data, so what an agency sees matches what your program did.

We are subject to this ourselves. Paramify holds its own FedRAMP 20x certification, which means December 7 and March 7 are on our calendar too. More detail is on our VDR and VER compliance page.

VDR AND VER DEADLINES

Three months of grace is not three months of runway.

Paramify labels every finding with PAIN, reachability and exploitability, and produces the reports your agency customers will be asking for from December 7.

Start Your Free Trial

Next Steps: Get VDR/VER by the deadline

December 7 starts a grace period, and March 7, 2027 ends it. Losing certification can cost you contracts. To meet it, every finding needs its PAIN rating, reachability, and exploitability as soon as it comes in, and your monthly reports should come from that same record. 

Paramify does this from your scan data, using your environment’s architecture and the timeframes for your class. Book a demo ASAP to see how it works for your program.

Frequently asked questions

Do I lose my FedRAMP certification on December 8, 2026? 

No. Missing it puts you into a grace period that runs to March 7, 2027, during which you keep your certification and operate under a corrective action plan.

Can the grace period be extended? 

No. FedRAMP states there are no extensions past the end of the default grace period and that it applies regardless of notification, corrective action, or progress.

What happens after March 7, 2027? 

An offering not following the VDR and VER rules by that date loses its FedRAMP Certification until it does follow them. FedRAMP revokes the certification with public notice.

Can I get certification back after it is revoked? 

Yes. FedRAMP takes no other punitive action, and offerings that lose certification this way can regain it by demonstrating they are following the rules.

Does this apply to Rev 5 providers too? 

Yes. The VDR and VER rulesets carry the same dates and the same remediation timeframes on both the Rev 5 and 20x paths. The exception is Class A, where neither ruleset is published.

Watch the full video walkthrough: What Happens If You Miss the December 7 VDR Deadline?

Learn More:
Isaac Teuscher
A Security Engineer leading the technical implementation of cloud and AI-driven security. With experience in NIST 800-53 and FedRAMP, Isaac collaborates with executive teams to build scalable security programs that meet the highest federal compliance standards.
Oct 2026
Related posts

Paramify blog

Interviews, tips, guides, industry best practices, and news.

Understanding BOD 26-04 and FedRAMP VDR: What You Need to Do to Stay Compliant

CISA’s BOD 26-04 moves federal agencies to risk-based vulnerability response, and FedRAMP providers must adopt VDR and VER to support it. This guide explains how the two map to CISA’s four risk factors and what to change in your process to stay compliant.
Read post

What Are FedRAMP VDR and VER? The Difference, the Deadline, and the PAIN Scale

FedRAMP VDR covers finding and fixing vulnerabilities on an ongoing basis. VER covers rating each one on likely exploitation, internet reachability, and potential agency impact (PAIN levels N0 to N5), with remediation deadlines set by those ratings and your certification class. Both are mandatory for legacy FedRAMP and FedRAMP 20x Class B and C providers by December 7, 2026, with a grace period that ends March 7, 2027.
Read post

FedRAMP 20x Self-Check Requirements: Class A, B, and C

FedRAMP’s 20x self-checks list what a Class A, B, or C certification package needs and what your Security Decision Record has to show. This article puts those requirements in one place, with the sample schemas and an at-a-glance comparison of the three classes.
Read post

Frequently Asked Questions

Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Can compliance advisors or consultants work in Paramify with us, and does it help with managed-service models?

Absolutely. Paramify is used by many advisory partners, RPOs, and MSPs to guide, generate, and manage documentation, perform gap assessments, facilitate policy/procedure drafting, and oversee remediation activities. Advisors can fill out templates, manage controls, and generate client-ready documents.

‍

We have privacy or compliance concerns, can we restrict what external reviewers can access?

Yes, you can assign role-based access controls in Paramify. Advisors or auditors can be given access only to certain programs, assessment and their related evidence.

Sensitive information can be withheld or redacted as needed, and only certified reviewers see specific items.

‍

Can auditors or advisory partners get direct access to our Paramify environment, or do we have to export everything for them?

Yes, Paramify allows external assessors/auditors and advisors to be invited as users, with controlled permission levels. They can review specific evidence, policies, SSPs, POA&Ms, or assessment modules without accessing broader company data. 

Documentation — such as Appendix A, SSPs, procedures, and POAMs — can also be exported in multiple standard formats (Word, Excel, OSCAL, EMASS, PDF) as needed.

Can I get matched with an Advisor based on my specific needs?

Yes. You can use the Get Matched feature on our website. We will review your specific compliance goals and connect you with the partner best suited for your industry and timeline.

How do Advisors use Paramify during a FedRAMP engagement?

Advisors use Paramify to conduct Gap Assessments, map controls, Automate SSPs, and manage POA&Ms.

Instead of spending months writing Word documents, the Advisor inputs the system architecture and control implementations into Paramify, which then generates the required NIST-formatted documentation.

Does Paramify compete with its Advisors?

No. Paramify is a software company. We do not offer independent audit or long-term consulting services. Our goal is to empower Advisors with better tools so they can serve more clients effectively.

‍

What are the different partner tiers?

We feature Premier Partners prominently on our site. These are firms that have demonstrated a high level of proficiency with the Paramify platform and have successfully helped many clients through the certification process using our tools.

How do I become an official Paramify Advisor Partner?

We look for firms with a proven track record in federal compliance. If you are interested in joining our network and leveraging our automation products, you can reach out via our contact page or schedule a demo to see how our tools fit into your workflow.

What is the benefit of using an Advisor who uses Paramify vs. one who doesn't?

Advisors using Paramify can accelerate your implementation and typically deliver documentation in a fraction of the time it takes without Paramify. This means:

  • Faster Implementation: An accelerated implementation roadmap keeps timelines predictable.
  • Lower Costs: Reduced manual consultant hours.
  • Higher Accuracy: Automation eliminates the "copy-paste" errors common in traditional SSPs.‍
  • Easier Maintenance: Your Advisor can help you manage POA&Ms and continuous monitoring within the platform.
Does working with an Advisor on this list guarantee FedRAMP or CMMC authorization?

No firm can "guarantee" authorization, as the final decision rests with the government authorizing body (e.g., the FedRAMP PMO or the DoD).

However, working with a Paramify Advisor significantly reduces the risk of documentation errors and ensures your package is built on a technically sound, automated foundation.

‍

How do I choose the right Advisor for my organization?

Our Advisor page allows you to filter partners by their specific expertise, such as FedRAMP, CMMC, FISMA, or GovRAMP.

Why does Paramify partner with Advisors?

Paramify is an “Iron Man suit” for GRC experts. We provide automation technology to generate and manage compliance documentation (like SSPs snd POA&Ms) while Advisors provide the expert human oversight and implementation expertise.

Together, we offer a "best-of-both-worlds" solution: expert consulting powered by industry-leading automation and risk management planning.

What is the Paramify Advisor Partner Network?

The Paramify Advisor Partner Network is a curated group of cybersecurity and compliance firms — including CMMC Registered Practitioner Organizations (RPOs) and accredited Independent Assessors— that use Paramify’s platform to deliver faster, more accurate compliance outcomes for their clients.

I already have an advisor or very capable GRC team. Why do I need Paramify?

Use Paramify's Risk Solution platform to automate ATO packages, improving cost efficiency, speed, and accuracy. This frees your team to focus on more valuable efforts like security posture enhancement and compliance improvements.