In This Article
If you need to simplify compliance and risk management while meeting timelines and keeping your budget under control, Paramify has you covered. But, what does Paramify actually do?
Paramify is cloud-based software that automates risk-management processes for government agencies, cloud providers, and the Defense Industrial Base.
Paramify cuts through the chaos, boosts accuracy, and helps you get and stay audit-ready fast. Curious how it works? Let’s dive in.
What Does Paramify Do?
Paramify is a risk management platform that builds a single, living data model of your security posture, then uses that model to plan a compliance roadmap, sequence implementation work, and automatically produce any reporting required – including SSP, SDR, POA&Ms, VER/VDR, Trust Center — for compliance with government and commercial frameworks like FedRAMP, FISMA, CMMC, DoD ATO, GovRAMP, SOC 2, HIPAA, ISO 27001, HITRUST, and more.
Organizations that put real security first, not just compliance, choose Paramify. Your certification, the ATO letter, the auditor's signature: those happen when the underlying security is actually managed well.
Paramify is FedRAMP 20x Class C Certified, and customers like UberEther have cut compliance labor by 80% running on it.
Why Do FedRAMP Marketplace Companies Choose Paramify Above Other GRC Tools?
CISOs that take security seriously choose Paramify above all other GRC platforms. Paramify cuts out compliance busywork so you can focus on actually improving and maintaining premiere-level security.
Paramify automates the implementation tracking, documentation & reporting, and monitoring required to earn and keep federal and/or commercial security certifications. It covers every framework built on NIST 800-53 (FedRAMP, FISMA, RMF, DoD ATO across Impact Levels 2 through 6, GovRAMP, TX-RAMP) and NIST 800-171 (CMMC), plus SOC 2, HIPAA, ISO 27001, and HITRUST.
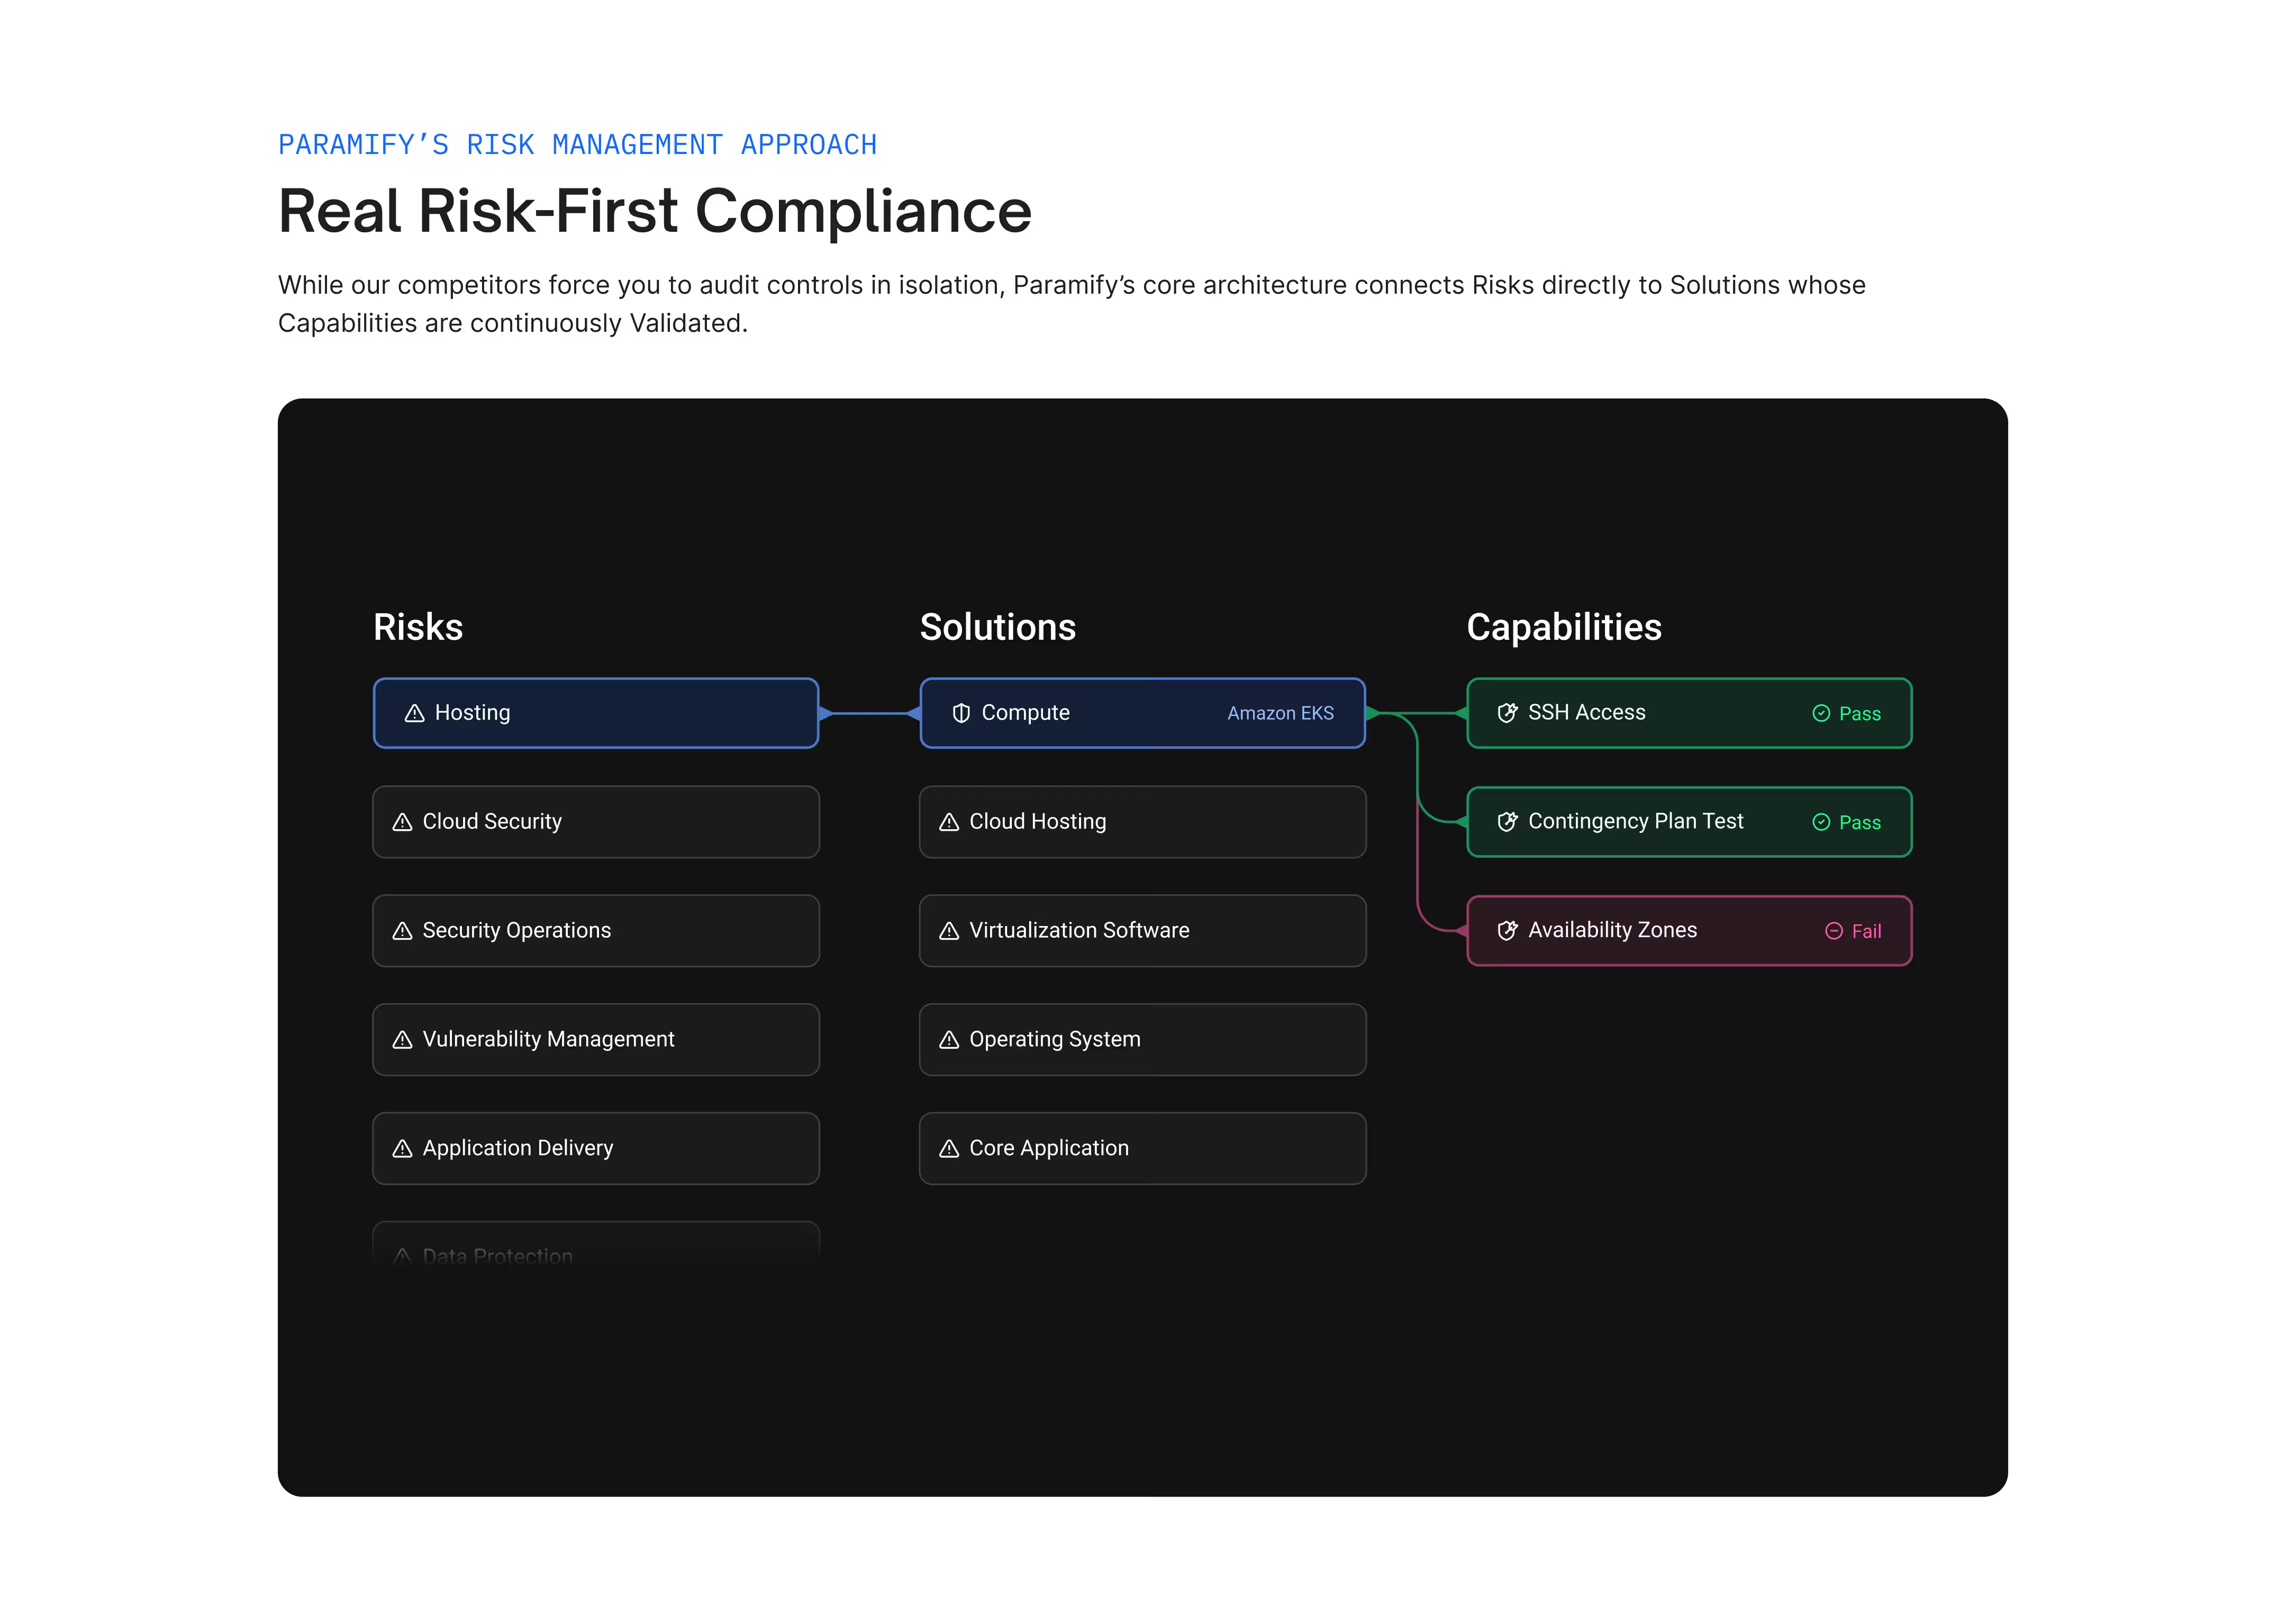
Instead of storing static documents, Paramify runs on a single, data-centric model of your organization: its people, systems, and controls. Update one fact, say that you rotated an encryption key, and it cascades across every framework that field touches. Anytime you make an update, it maps everywhere the change is relevant.
Work done for FedRAMP reuses automatically for SOC 2, CMMC, DoD, and GovRAMP, instead of your team re-answering the same question in five different spreadsheets and creating 5 different sets of static documentation.
What Makes Paramify Different?
Paramify is designed for people who care about real risk management, especially those who don’t want to do security theater.
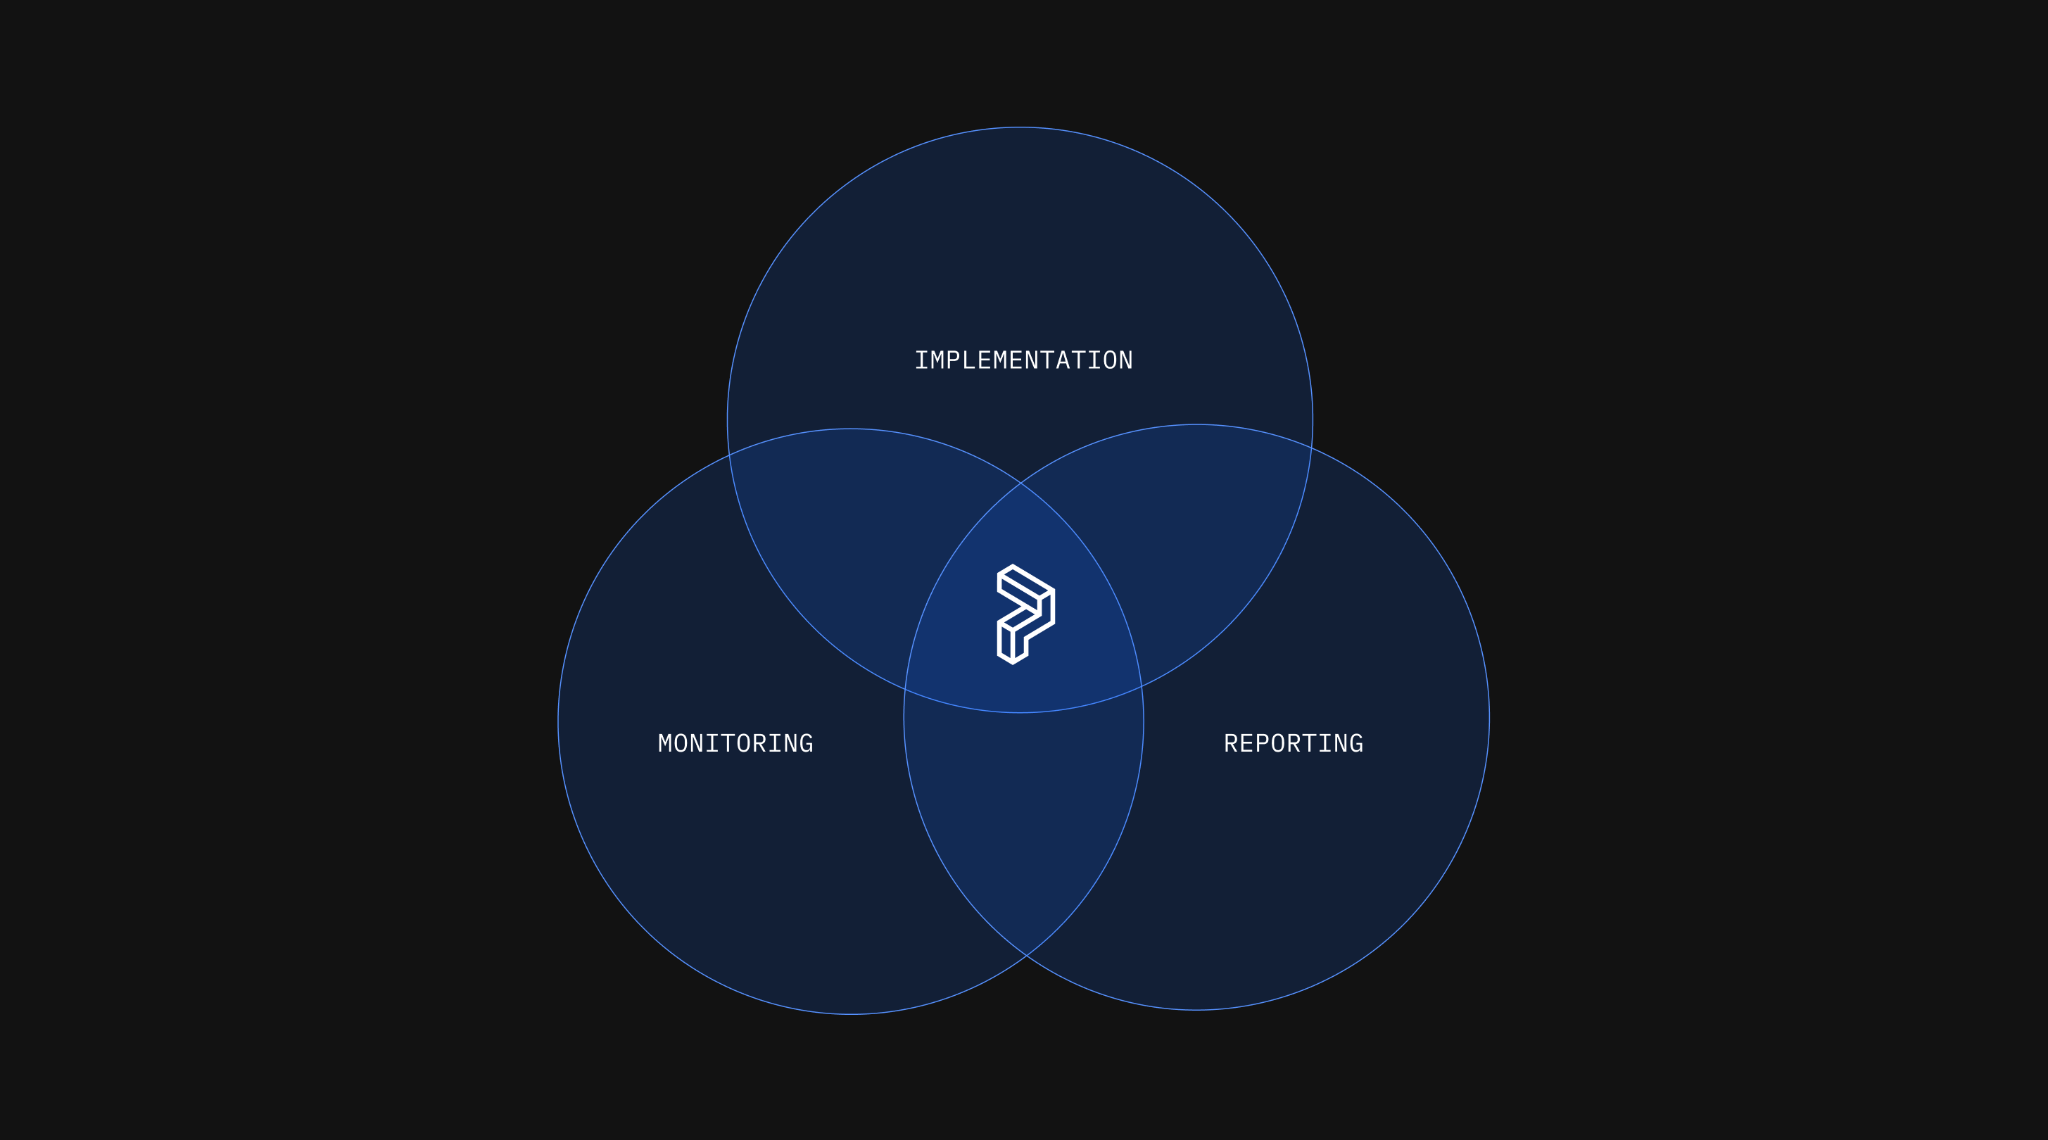
Paramify introduces a modern risk management method automating the busywork out of the entire lifecycle of implementation, reporting, and monitoring.
Whether your frameworks are federal, commercial, or both, you can now manage risk from one source. Individual updates map across different frameworks and automatically create any required reports.
Risk and compliance requirements are always changing, especially now that the time to exploit vulnerabilities is shrinking. Managing these changes is exhausting and time consuming. Paramify handles tracking of compliance changes and guides you through the changed risks.
→ Watch: Modern Security Package Management
How Does Paramify Cover the Full Risk Management Lifecycle?
Implementation
An hour-long kickoff maps your existing stack (AWS, Okta, CrowdStrike, and whatever else you already run) to the controls of your target framework(s), converting that data into a prioritized gap assessment and compliance roadmap from day one.
As your tech stack and threat environment evolve, Paramify continuously recalibrates your controls and updates risk priorities in real time so your strategy stays aligned.
Your compliance roadmap adjusts as your technology stack and threat environment shift. Whenever new applications are integrated or regulatory mandates change, Paramify automatically updates your risk posture and maps control requirements, enabling your organization to operate from a live, prioritized execution strategy.
By pushing implementation straight into Jira or ServiceNow through native integrations, Paramify connects strategy directly to implementers so fixes get done efficiently.
→ Get your security strategy and roadmap: Request a gap assessment
Monitoring (Evidence Collection & Validation)
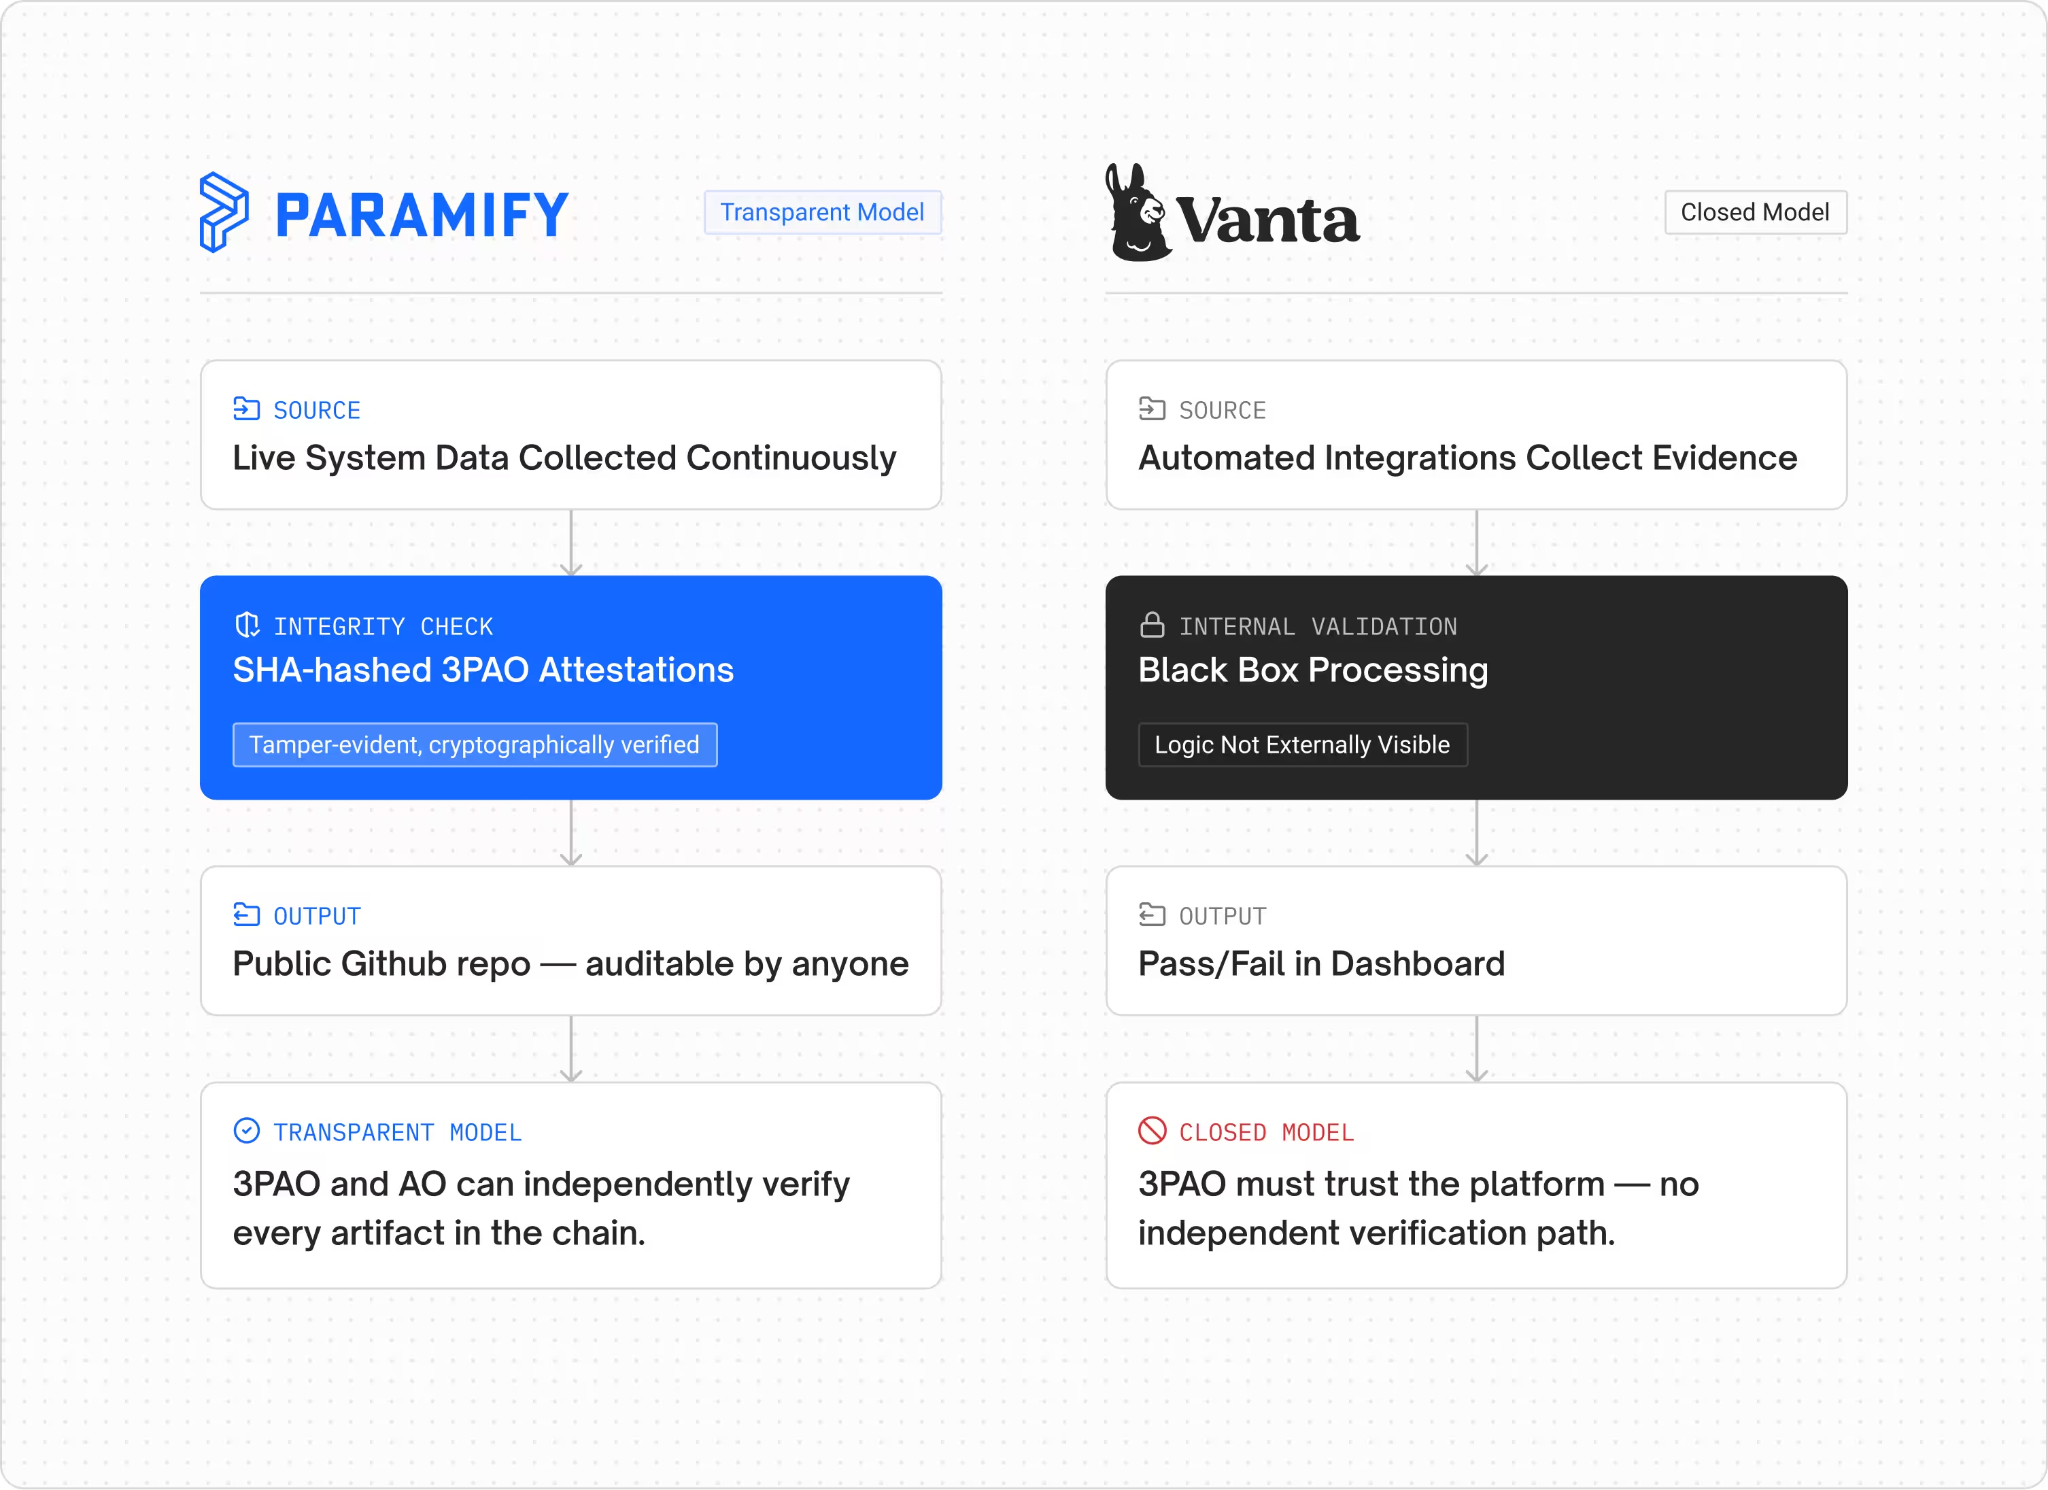
Evidence collection and validation can be fully automated using Paramify’s TUI and API Library, returning pass, fail, or partial statuses before a manual review even begins.
You’ll continuously get live, telemetry-backed evidence collection and automated validator logic to verify your system state.
Unlike GRC software like Vanta or Drata, Paramify uses SHA-hashed Independent Assessor attestations with submissions maintained in a public GitHub repository. The record is open, independently verifiable, and survives Paramify as a company.
→ See automated evidence collection and validation in action:
Reporting (Compliance Deliverables)
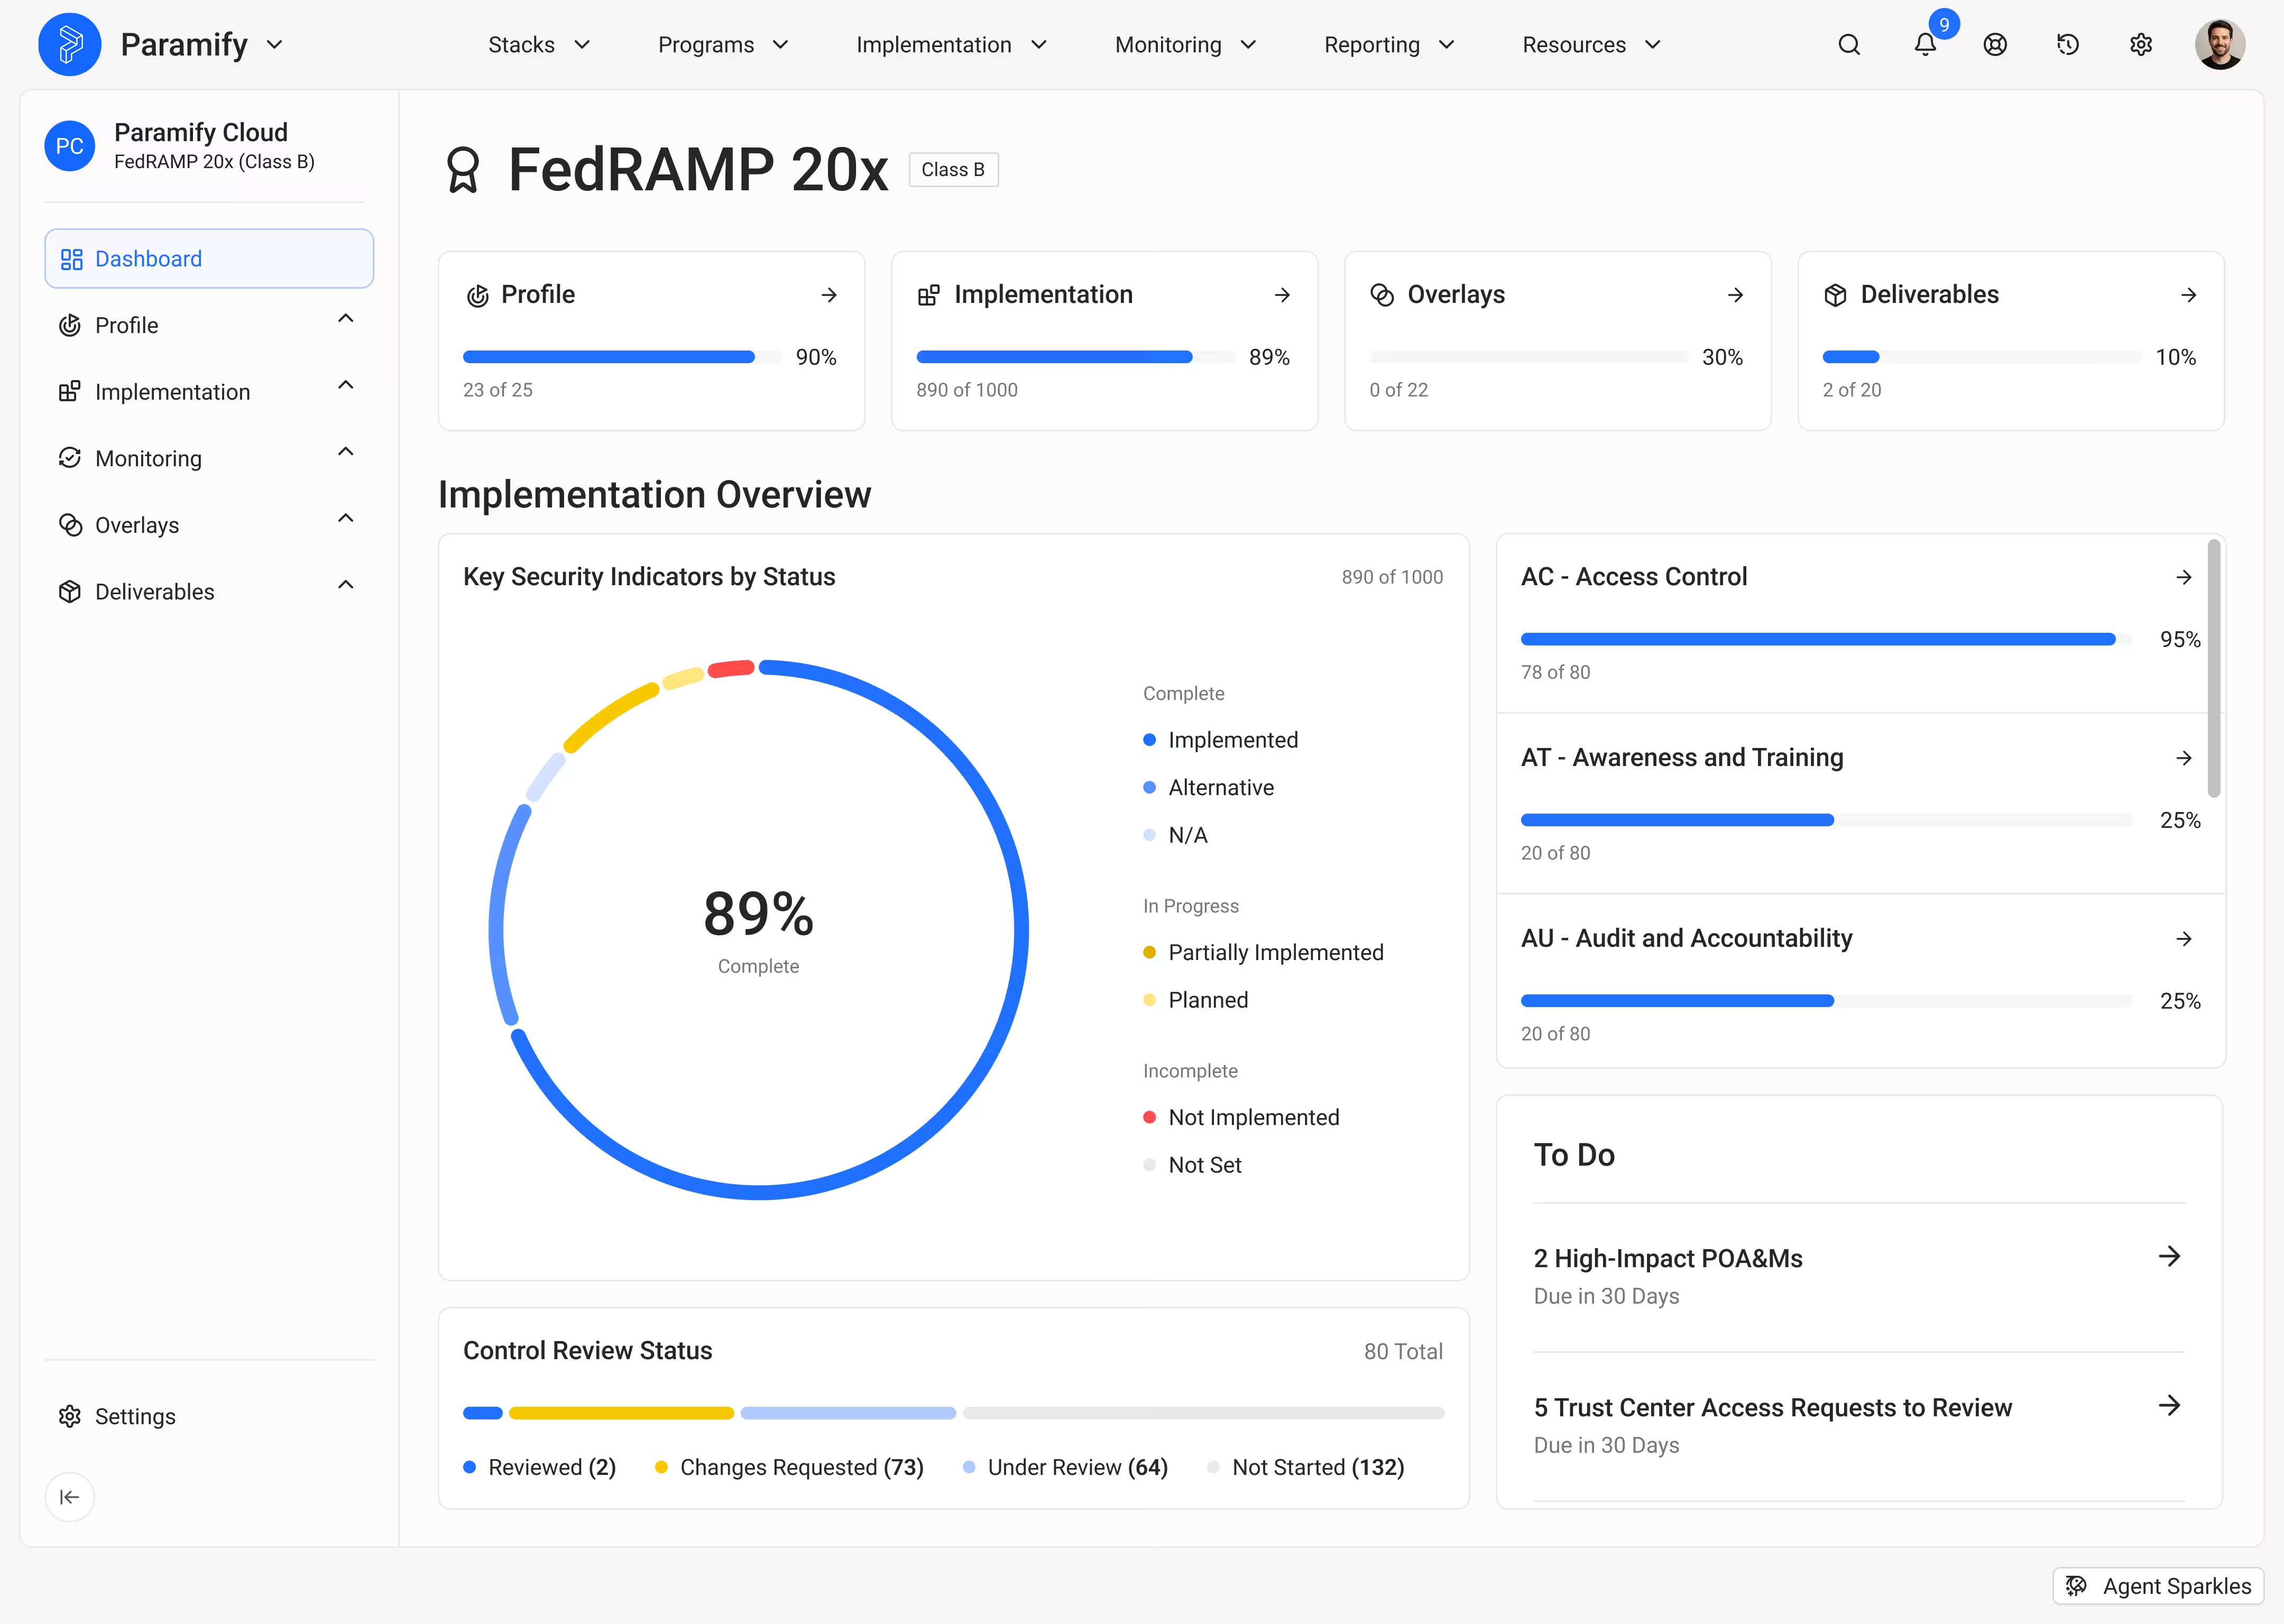
Paramify automatically generates reporting that reflects the current state of your security, not a static, point-in-time snapshot of what you hope your security is like.
At any time you can use Paramify to generate the documentation required for your framework(s). Instantly get accurate SDRs, SSPs, Trust Center, VDR/VER, Policies & Procedures, POA&Ms and more.
For FedRAMP 20x customers, a live Trust Center continuously publishes compliance status on an ongoing basis rather than just at audit time.
Is Paramify Right for You?
Paramify is not the best choice for every organization. Here’s how you can know if it’s the best fit for you:
- You’re serious about security. If your business is looking for check-box compliance systems so you can get a sticker and make the sale, we are not for you. If you want to build genuinely great security the most efficient way possible, let’s talk.
- You're building for federal and/or regulated markets. If you're chasing a generic compliance badge with no regulated framework requirement behind it, there’s likely a cheaper solution.
- You’re looking for the best solution for FedRAMP 20x or CR26 for Legacy FedRAMP. Paramify is the #1 GRC tool to meet new FedRAMP 20x and CR26 requirements because it was built for 20x and CR26, rather than tacking on these capabilities.
What Results Do Paramify Customers See?
UberEther, an identity and access management firm specializing in FedRAMP High and DoD Impact Level 5 authorizations, replaced 15 years of manual compliance workflows with Paramify. Generating a full SSP Appendix A and 36 core policy documents dropped from more than 20 hours of manual work to 30 seconds, an 80% reduction in labor hours for security documentation. Per-employee customer capacity jumped 400%, moving staff from supporting 1 to 2 customers to 6 to 8. Audit check-ins shrank from 8-hour marathons to 2-hour sessions with zero findings, and UberEther realized value in 3 days instead of the typical 90.
Vbrick and Mirai Security saw similar results. Vbrick, moving from a legacy FedRAMP Class B (Low) Authorization to FedRAMP 20x, priced out what building that continuous-evidence tooling by hand would take on top of a team already stretched thin by Rev 5, and landed on needing one or two more full-time hires just to keep pace. Paramify avoided that hire: VP of Cloud Operations Todd Kistner now saves close to a day of work a week, and the annual scramble, entire holiday weekends lost to writing documentation, is gone.
Enterprise cloud service providers including Keeper Security, Qualys, Trellix, Elastic, Okta, Adobe, and Akamai run some or all of their compliance programs through Paramify.
→ See more user testimonials and Paramify case studies
Does Paramify Replace My GRC Advisor?
No, and it isn't trying to. Paramify sequences your implementation work, tells you what to build in what order, and generates any reporting you need to prove it. It doesn't make judgment calls specific to your risk posture, and it doesn't do the hands-on remediation engineering itself.
A network of GRC advisors and consulting partners uses Paramify to do that work faster and pass the time savings on to their clients: UberEther's numbers above are one example.
→ Working with an advisor or MSP: Does Paramify replace a GRC advisor?
→ Need one: Request a list of advisors using Paramify
→ Advising clients yourself: Partner with Paramify
How Is Paramify Deployed, and What Does It Cost?
Paramify runs as SaaS or self-hosted, depending on your environment's requirements.
We believe in a transparent pricing model, so you can compare when you shop around for GRC tools. How much you pay for Paramify will depend on your data impact level, framework, and whether you need continuous monitoring support.
Ready to Simplify Your Security Risk Management and Compliance?
Paramify is built to be the faster, cheaper, and more accurate Risk Management automation tool. Customer success at organizations like UberEther and Vbrick are the proof.
- Request a gap assessment to quickly see your risk management gaps by framework.
- Request a demo below to see the living dashboard in action.
- Check current pricing for your framework and impact level.
FAQ
What frameworks does Paramify support?
Everything built on NIST 800-53 (FedRAMP, FISMA, DoD ATO across Impact Levels 2–6, GovRAMP, TX-RAMP) and NIST 800-171 (CMMC), plus SOC 2, HIPAA, ISO 27001, and HITRUST.
Is Paramify itself FedRAMP certified?
Yes, at Class B (Low) and Class C (Moderate). See Paramify's listing on the FedRAMP Marketplace.
Does Paramify replace my GRC advisor or consultant?
No. Paramify sequences your implementation work and generates documentation once it's built, but it doesn't make judgment calls on your specific risk posture or do hands-on remediation. GRC advisors use Paramify to do that work faster.
Can I get FedRAMP certified without an agency sponsor now?
Yes. FedRAMP 20x dropped the agency sponsorship requirement that defined the Legacy Rev 5 process, and FedRAMP Ready is being retired as a standalone track. 20x is now the default on-ramp for a CSP without a sponsor lined up.
Is Paramify available self-hosted, or only as SaaS?
Both. Paramify runs as SaaS or self-hosted, depending on your environment's requirements.
How long does it take to see value from Paramify?
An hour-long kickoff produces a gap assessment and roadmap on day one. UberEther realized full value in 3 days; Transform9 submitted a complete FedRAMP 20x package in 8 days after switching to Paramify.
What does FedRAMP 20x's continuous assessment requirement actually mean?
Instead of proving your controls work once, at audit time, you keep proving it, tracked against Key Security Indicators (KSIs) with automated, production-derived evidence rather than a narrative claim. Paramify pulls that evidence directly from the systems you run, validates it automatically as pass, fail, or partial, and publishes current status through a Trust Center instead of a static, point-in-time document.
What is a Trust Center, and does Paramify provide one?
A Trust Center publishes an organization's current compliance status on an ongoing basis, instead of only at audit time. Paramify's Trust Center is built for FedRAMP 20x's continuous assessment requirements and runs off Paramify's OSCAL-native data model.
Does Paramify integrate with Jira or ServiceNow?
Yes, through MCP-powered integrations that push implementation and remediation tasks directly into the tools engineering and DevOps teams already use.
How much does Paramify cost?
Cost depends on your data impact level, framework, and whether you need continuous monitoring support. Current tiers and ranges are on Paramify's pricing page.
Who actually uses Paramify?
Enterprise cloud service providers (Keeper Security, Qualys, Trellix, Elastic, Okta, Adobe, and Akamai among them), GRC advisory firms like UberEther, and SMBs managing multiple frameworks without a large compliance team.